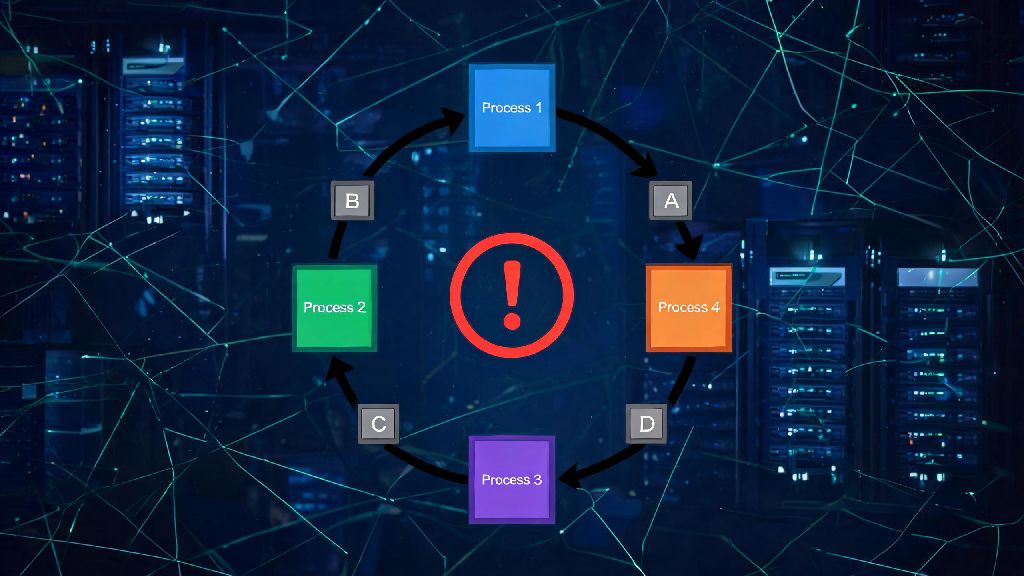
If you’ve ever spent hours troubleshooting a frozen app or unresponsive database, you’ve almost certainly run into a deadlock at some point. Most people discuss deadlocks as a performance nuisance, but far fewer stop to ask: are deadlocks secure, or do they open up unexpected gaps for malicious actors or system failure? This guide breaks down the security implications of deadlocks, common use cases where they pop up, and steps you can take to keep your systems protected without sacrificing functionality.
Are Deadlocks Secure by Default?
To answer this question, we first have to cover the core nature of deadlocks: they occur when two or more processes each hold a resource the other needs to complete its task, and neither will release its held resource first. This creates a permanent standstill that freezes all affected processes until an external action breaks the deadlock. By default, deadlocks are not secure, even if they don’t seem to cause immediate harm beyond slow performance. If you’ve only ever thought of deadlocks as a performance issue, you’re not alone — even many junior devs never stop to ask are deadlocks secure until they face a related security breach.
Unhandled deadlocks are one of the top 10 causes of unplanned system downtime for small to mid-sized applications, per recent cloud infrastructure reports. Beyond downtime, deadlocks can leave partial operations unfinished, which can corrupt data if transactions aren’t rolled back properly. For example, if a payment processing deadlocks mid-transaction, you might have a user charged but their order not marked as paid, which creates both fraud risks and customer trust issues that can take months to repair.
Common Scenarios Where Deadlocks Create Security Gaps
Deadlocks don’t just appear out of nowhere. They almost always stem from poor resource allocation logic, or gaps in how you set priority for competing processes. The most high-risk scenarios where deadlocks lead to security issues include:
Many real-time app teams miss these risks because they prioritize smooth user experience over edge-case error handling, especially for casual gaming platforms that see spikes in traffic during peak hours. For example, teams running casual card game platforms often run into deadlock issues when thousands of users join simultaneous tournaments, and Rummy888 has publicly shared past postmortems of how deadlocks in their match-making system temporarily locked 12% of active users out of their accounts a few years back. This example is a perfect reminder that even teams that prioritize user experience need to ask are deadlocks secure as part of their regular security audits. Their team noted that the worst impact wasn’t just user frustration, but that the deadlock left temporary session tokens exposed for 45 minutes before the issue was patched, putting user account data at low but measurable risk.
How to Minimize Security Risks From Deadlocks
You don’t have to eliminate every single possible deadlock to keep your systems secure — in fact, trying to do that often leads to overcomplicated code that creates more security gaps than it fixes. When you’re building your deadlock handling policy, the core question to keep front of mind is are deadlocks secure for your specific use case, not just how to eliminate them entirely. The first step is to implement regular deadlock detection scans, set to run every 30 to 60 seconds for high-traffic systems.
Automatic deadlock recovery protocols should always prioritize rolling back incomplete transactions first, before terminating idle processes, to avoid data corruption or partial request completion. You should also implement resource ordering rules for all processes that access shared resources: if every process requests resources in the same predefined order, you can eliminate 90% of unintended deadlocks before they happen. For teams that manage user-facing apps, make sure you have a dedicated alert set for unexpected deadlock spikes, as a sudden increase in deadlocks is often an early sign of a malicious actor trying to trigger a denial of service attack.
When Can Deadlocks Actually Be Part of a Secure System?
It’s easy to assume all deadlocks are bad, but in some specific cases, intentional deadlocks are used as a security control. For example, some secure access systems will trigger a deadlock on a user account if it detects 10+ failed login attempts in a row, locking both the user and any potential attacker out of the account until an admin reviews the activity. One of the most common questions we get from dev teams when talking about intentional deadlocks is are deadlocks secure enough to use as a regular security control, and the short answer is only if you have strict guardrails in place.
Intentional deadlocks are only safe if you have clear, automated recovery steps that don’t leave sensitive data exposed during the lock period. You should never use intentional deadlocks for systems that process real-time transactions or handle emergency services, as the downtime they create will do more harm than good. If you do choose to use intentional deadlocks as a security measure, make sure you test them regularly to confirm they don’t leak data or create larger system-wide deadlocks that impact other unrelated users.
At the end of the day, the answer to are deadlocks secure depends entirely on how you detect, handle, and plan for them. Unintentional, unhandled deadlocks are almost always a security risk, as they create denial of service gaps, data corruption risks, and potential exposure of sensitive user data. But when paired with clear recovery protocols and intentional design, even deadlocks can be used as a minor security control for low-risk use cases. Take the time to audit your current deadlock handling protocols at least once a quarter, and you’ll avoid most of the common security pitfalls associated with these common system errors.