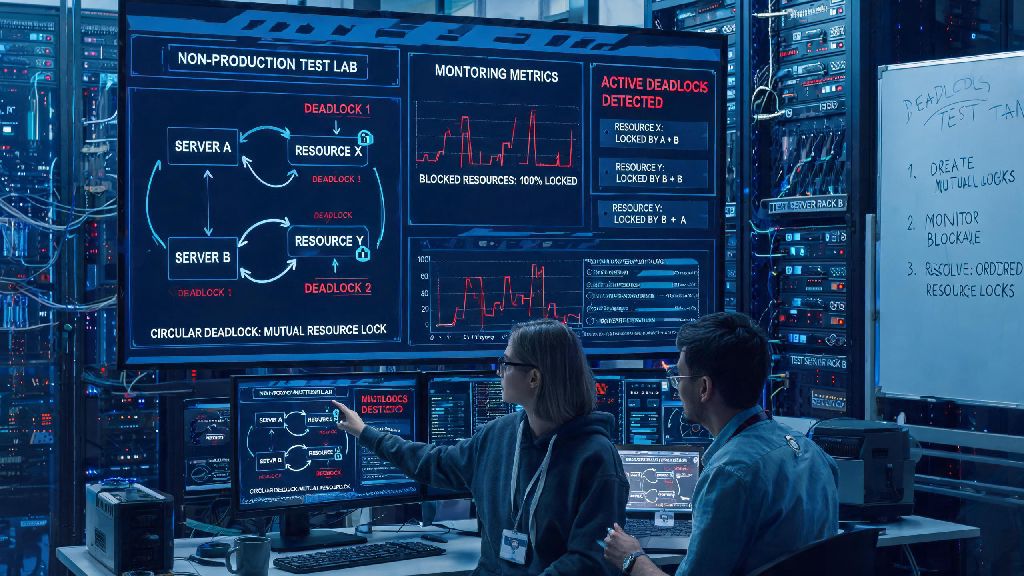
If you’ve ever spent hours debugging a random deadlock that took down your production e-commerce checkout, you’ve probably wondered: can i invite people to deadlock on purpose to test your system’s response? As a DevOps engineer with 7 years of experience building and testing distributed systems, I’ve run dozens of controlled deadlock tests with cross-functional teams, and the short answer is yes—if you follow strict guardrails to avoid costly mistakes. Most teams run these tests to validate their deadlock detection tools, recovery workflows, and team response time before an unplanned deadlock hits production. You don’t want to learn your detection alert is broken when 10,000 users are stuck mid-purchase, after all.
When It Makes Sense to Invite People to Deadlock Your Test Environment
Collaborative deadlock testing is only appropriate in controlled, non-production settings, and it serves very specific use cases for engineering and SRE teams. You might run this type of test if you’re rolling out new deadlock detection software, training new team members on deadlock response protocols, validating recovery scripts after a core system update, or testing database deadlock resolution for a new schema launch. When you plan to invite people to deadlock your test environment, you first need to make sure you meet all non-negotiable pre-requisites to avoid unnecessary disruption:
I once made the mistake of running a deadlock test on a semi-shared staging environment a few years back, and it knocked out the QA team’s test run for 3 hours. That’s why I always add one extra pre-check: send a 24-hour heads up to all teams that use the test environment before you start, so no one loses work mid-test. You don’t need a huge team for these tests either—usually 2 to 3 people is enough: one to trigger the deadlock, one to monitor detection alerts, and one to test recovery steps.
Core Risks of Inviting Multiple People to Trigger a Deadlock
Many teams underestimate how much chaos can happen when you invite people to deadlock a system without clear guardrails, and the costs of these mistakes can add up fast. The first and most common risk is uncontrolled deadlock spread—if multiple people trigger deadlocks across different system components at the same time, it can cascade to connected test services you didn’t account for. For example, if one person triggers a database deadlock and another triggers an operating system resource deadlock on the same server, the recovery scripts you prepared might not work for both issues at once.
Another risk is miscommunication: if someone triggers the deadlock earlier than planned, or forgets to announce they’re running the test, other team members might waste hours debugging a planned issue they think is unplanned. Permanent test environment corruption is also possible if the deadlock cuts off access mid-data write, especially if you’re working with unpatched legacy database systems. I’ve seen this happen once when a team ran an unplanned deadlock test on a test database that stored all their QA test user data, and they had to rebuild the entire database from scratch, which took 2 full days. The key to avoiding these risks is to assign a single test lead who owns the entire process, and makes all final calls about when to start, pause, or stop the test.
Step-by-Step Guide to Running a Collaborative Deadlock Test
Once you’ve checked all pre-requisites, you’re ready to invite people to deadlock the test environment following this simple, low-risk workflow. First, confirm your test environment is fully isolated, and create a full backup of all test data 30 minutes before the test starts. Next, share a clear run of show with all participants, so everyone knows their exact role, the timeline, and what signals to look for during the test.
Start with small, single-component deadlocks first before you bring in multiple people to trigger cross-system deadlocks. For example, first run a test where only one person triggers a simple database deadlock, and the rest of the team practices detecting and resolving it. Once the team is comfortable with that, you can move to more complex tests where multiple people trigger deadlocks across different parts of the system at the same time, to simulate a worst-case production scenario. Make sure you pause after each test to run a full retro: note what worked, what detection alerts didn’t fire, and how long recovery took, so you can improve your process for the next test. Don’t rush these tests—even a simple collaborative deadlock test should take at least 2 hours total, including prep and retro time.
Common Mistakes to Avoid With Collaborative Deadlock Testing
After running dozens of these tests, I’ve seen the same small mistakes lead to big disruptions over and over, and most are easy to avoid if you plan ahead. The biggest mistake by far is teams running these tests in production, even “small” ones. There is zero reason to trigger an intentional deadlock in production, no matter how small you think it is. Even if you think you can fix it fast, you never know what unexpected issues might pop up that could impact real users.
Another common mistake is not having a clear emergency stop button. Your emergency stop should be a single, one-click action that immediately kills all deadlocked processes and restores the test environment to its pre-test state. Don’t rely on manual recovery steps for emergency situations, because people panic under pressure and make mistakes. A third mistake is not documenting everything. You should track every part of the test: who participated, what deadlocks were triggered, how long detection took, how long recovery took, and any issues that came up. This documentation will be invaluable if you ever have to respond to a real production deadlock later. I also see teams forget to follow up on action items from the test retro. If you find out your detection alert takes 5 minutes to fire when it should take 10 seconds, don’t just note that down and forget it—fix the issue before your next test, or before a real deadlock hits.
At the end of the day, asking can i invite people to deadlock for testing purposes is a smart question for any team that wants to build more resilient systems. When done right, collaborative deadlock testing is one of the best ways to make sure your team is prepared for the inevitable unplanned deadlock that will hit production at some point. Just make sure you’re only running these tests in fully isolated environments, you have clear guardrails in place, and everyone on the team knows their role before you start. You don’t have to wait for a costly production outage to learn how well your deadlock response works—controlled testing with your team will help you fix gaps long before they impact real users.